Continuous NIS2 and GDPR compliance, without the consultant fee
Gap analysis against NIS2 Article 21 and GDPR, security awareness training for your staff, periodic check-ins, and supplier follow-up – in one platform.
Not sure if you're in scope? Take our 1-minute self-test →From 990 SEK/month, no lock-in. See all pricing
NIS2 and GDPR are included in the base price. Do you manufacture or sell products with digital elements? Our CRA (Cyber Resilience Act) module is available as an add-on.
Compliance map
- NIS2Article 21 · ten requirement areasIncluded
- GDPRLegal basis, rights, processor agreementsIncluded
- CRAProducts with digital elementsAdd-on
This is what it looks like
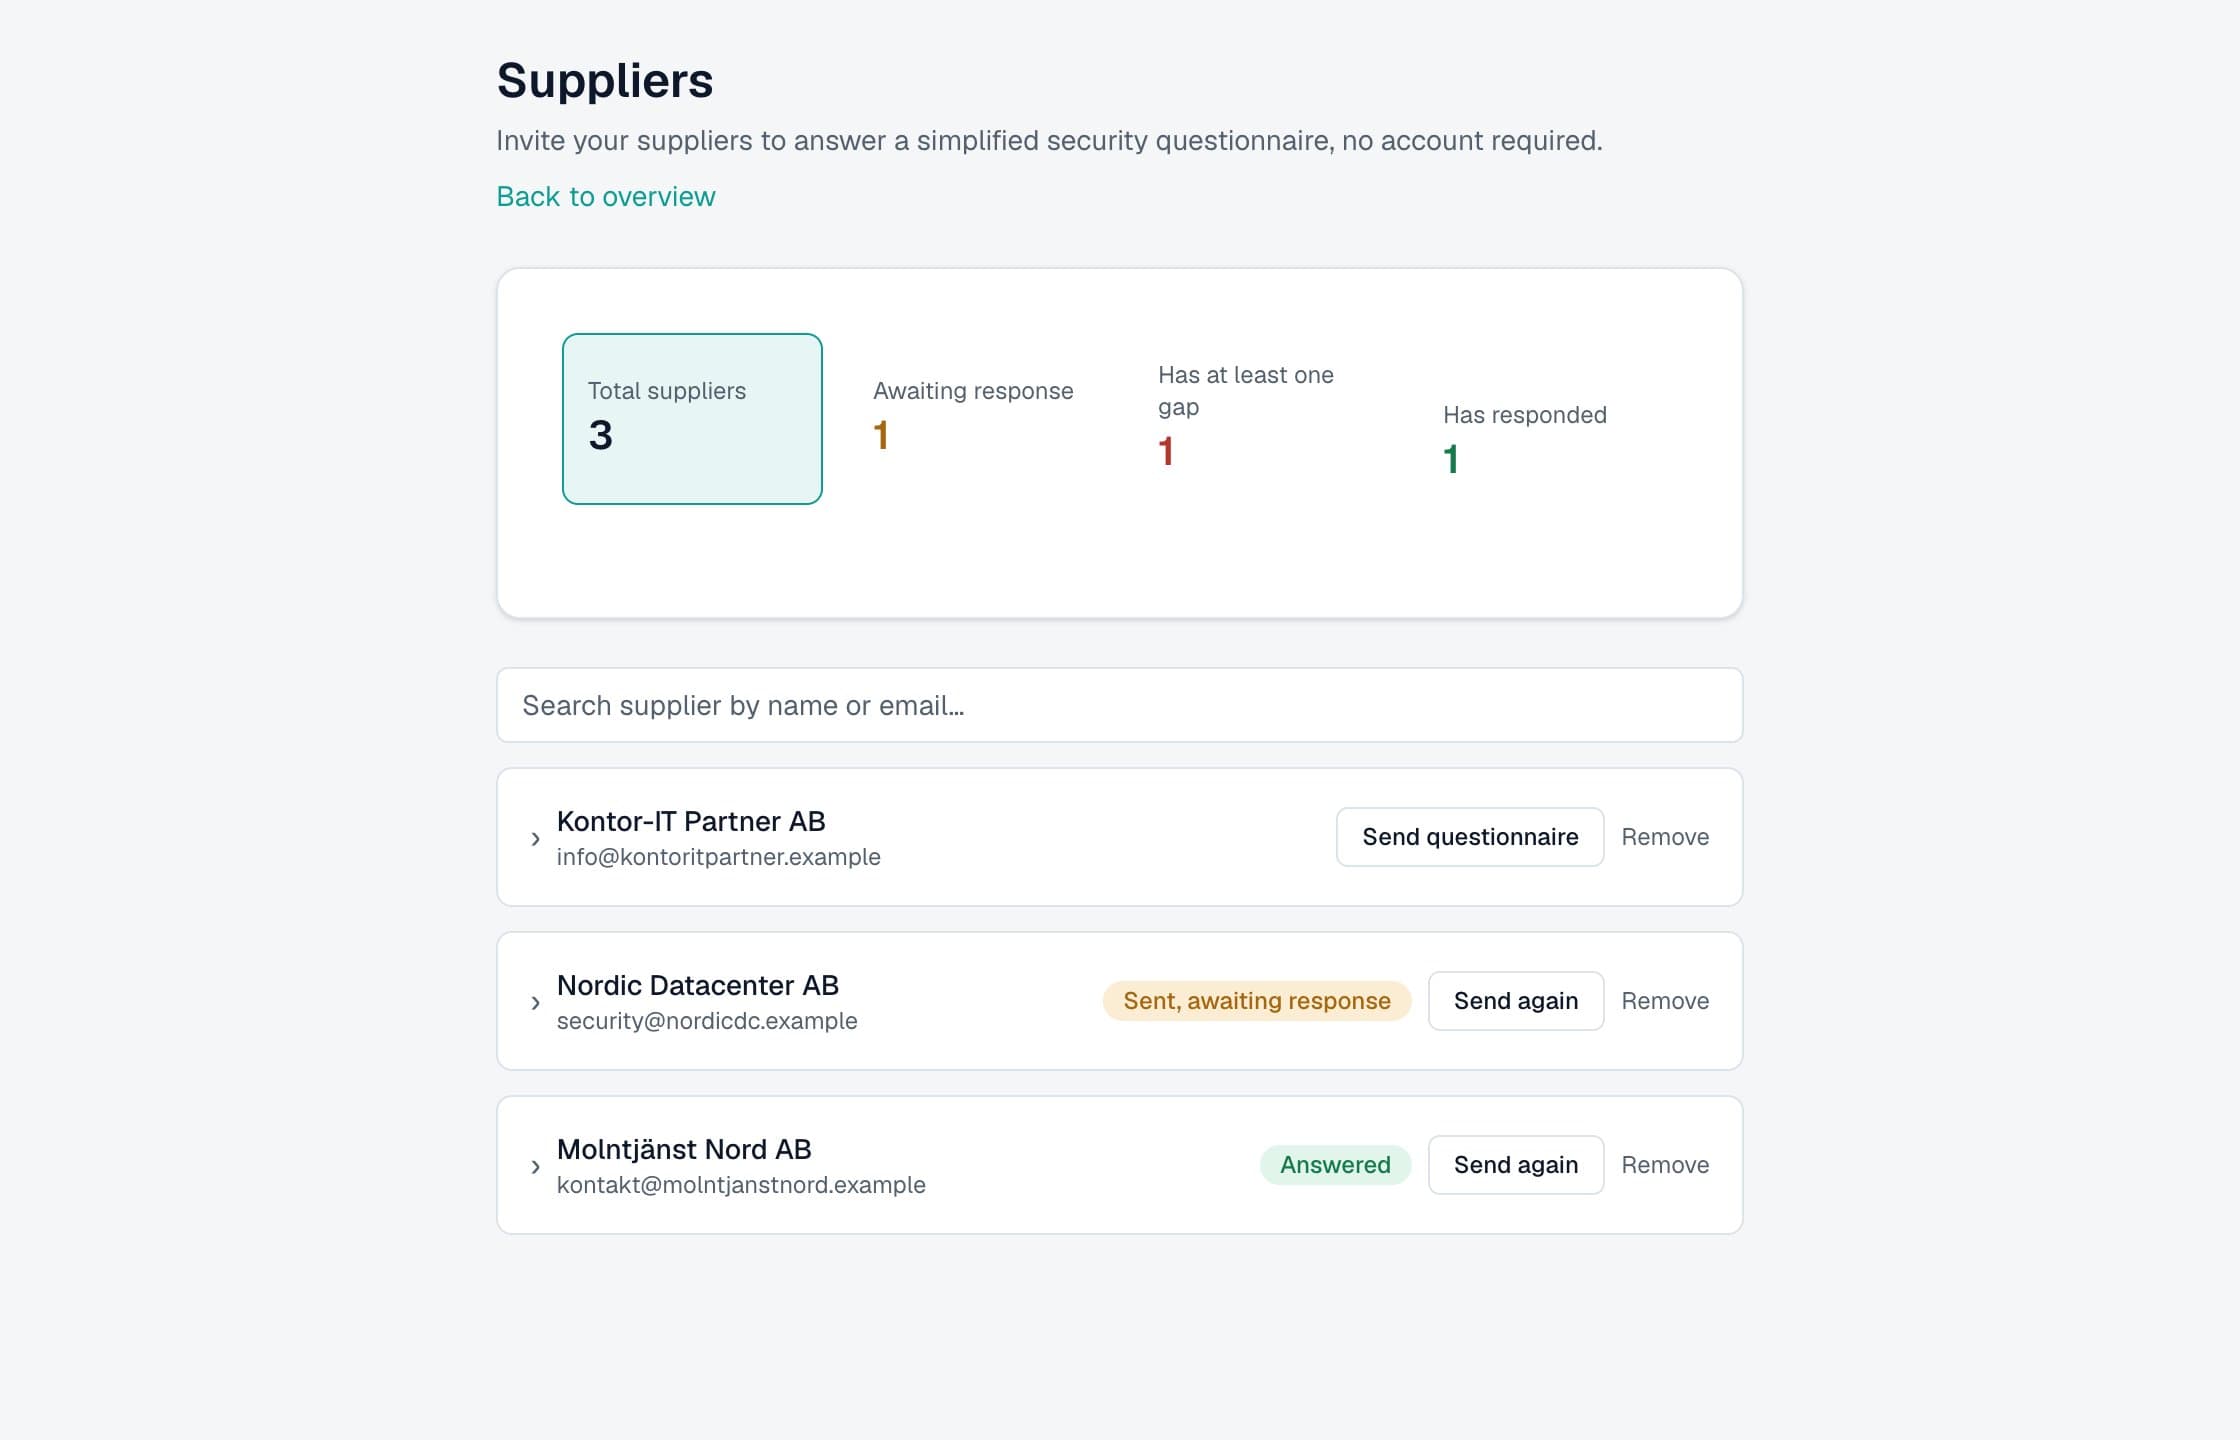
Real views from the platform, with sample data from a demo company.
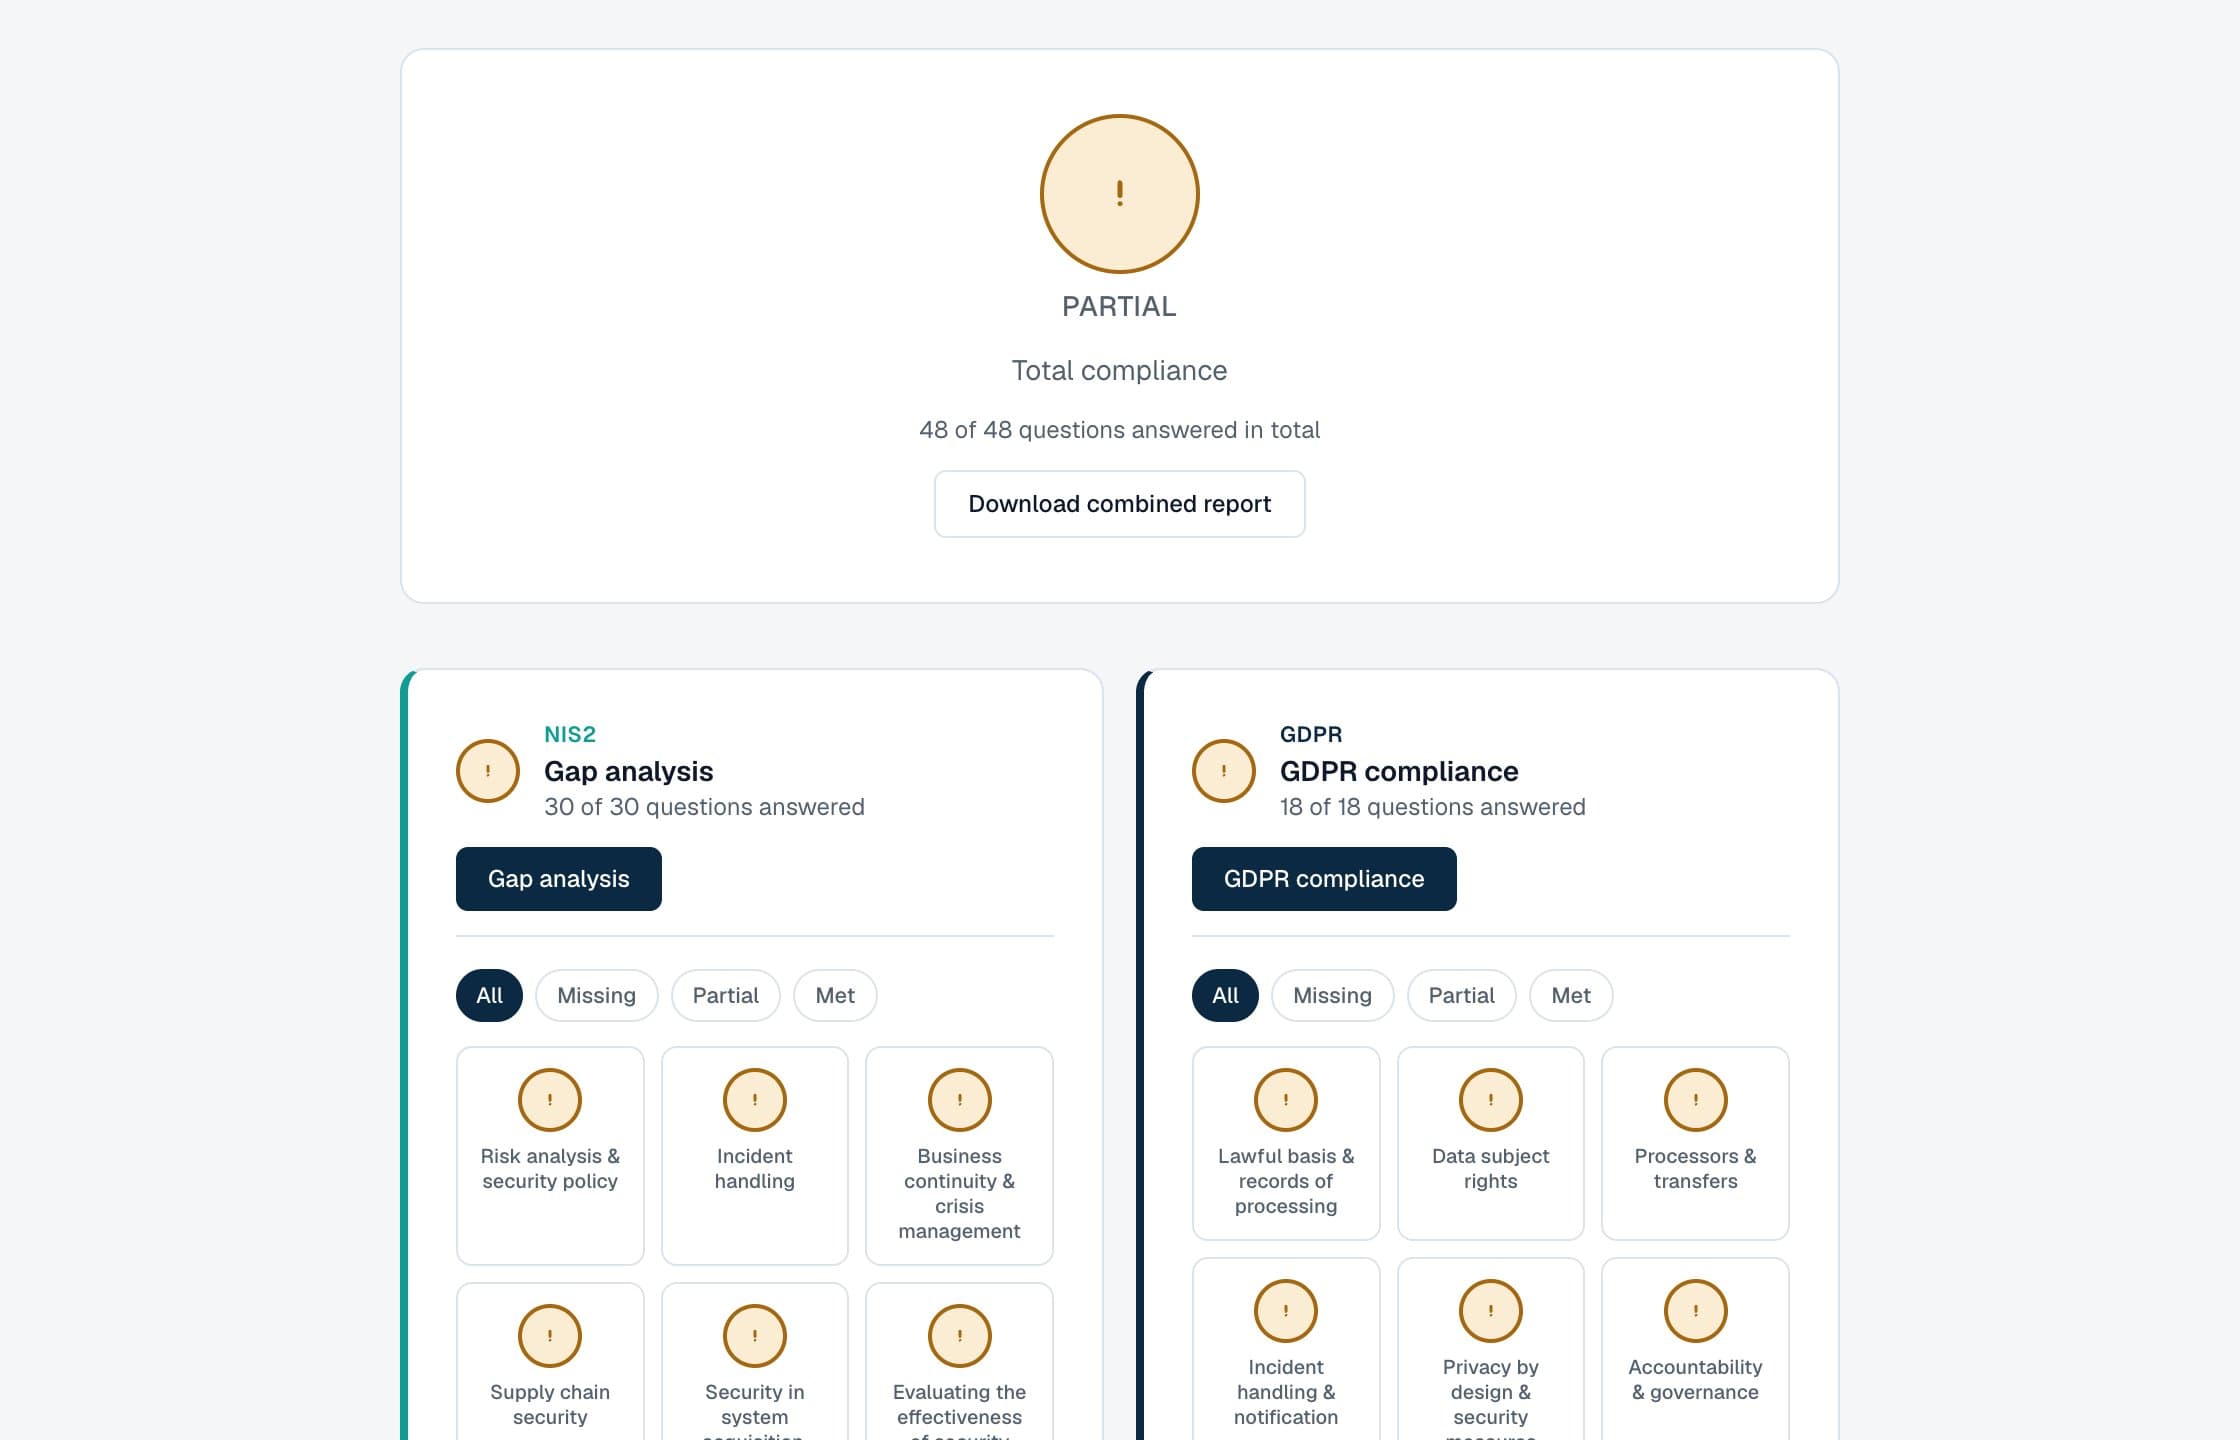
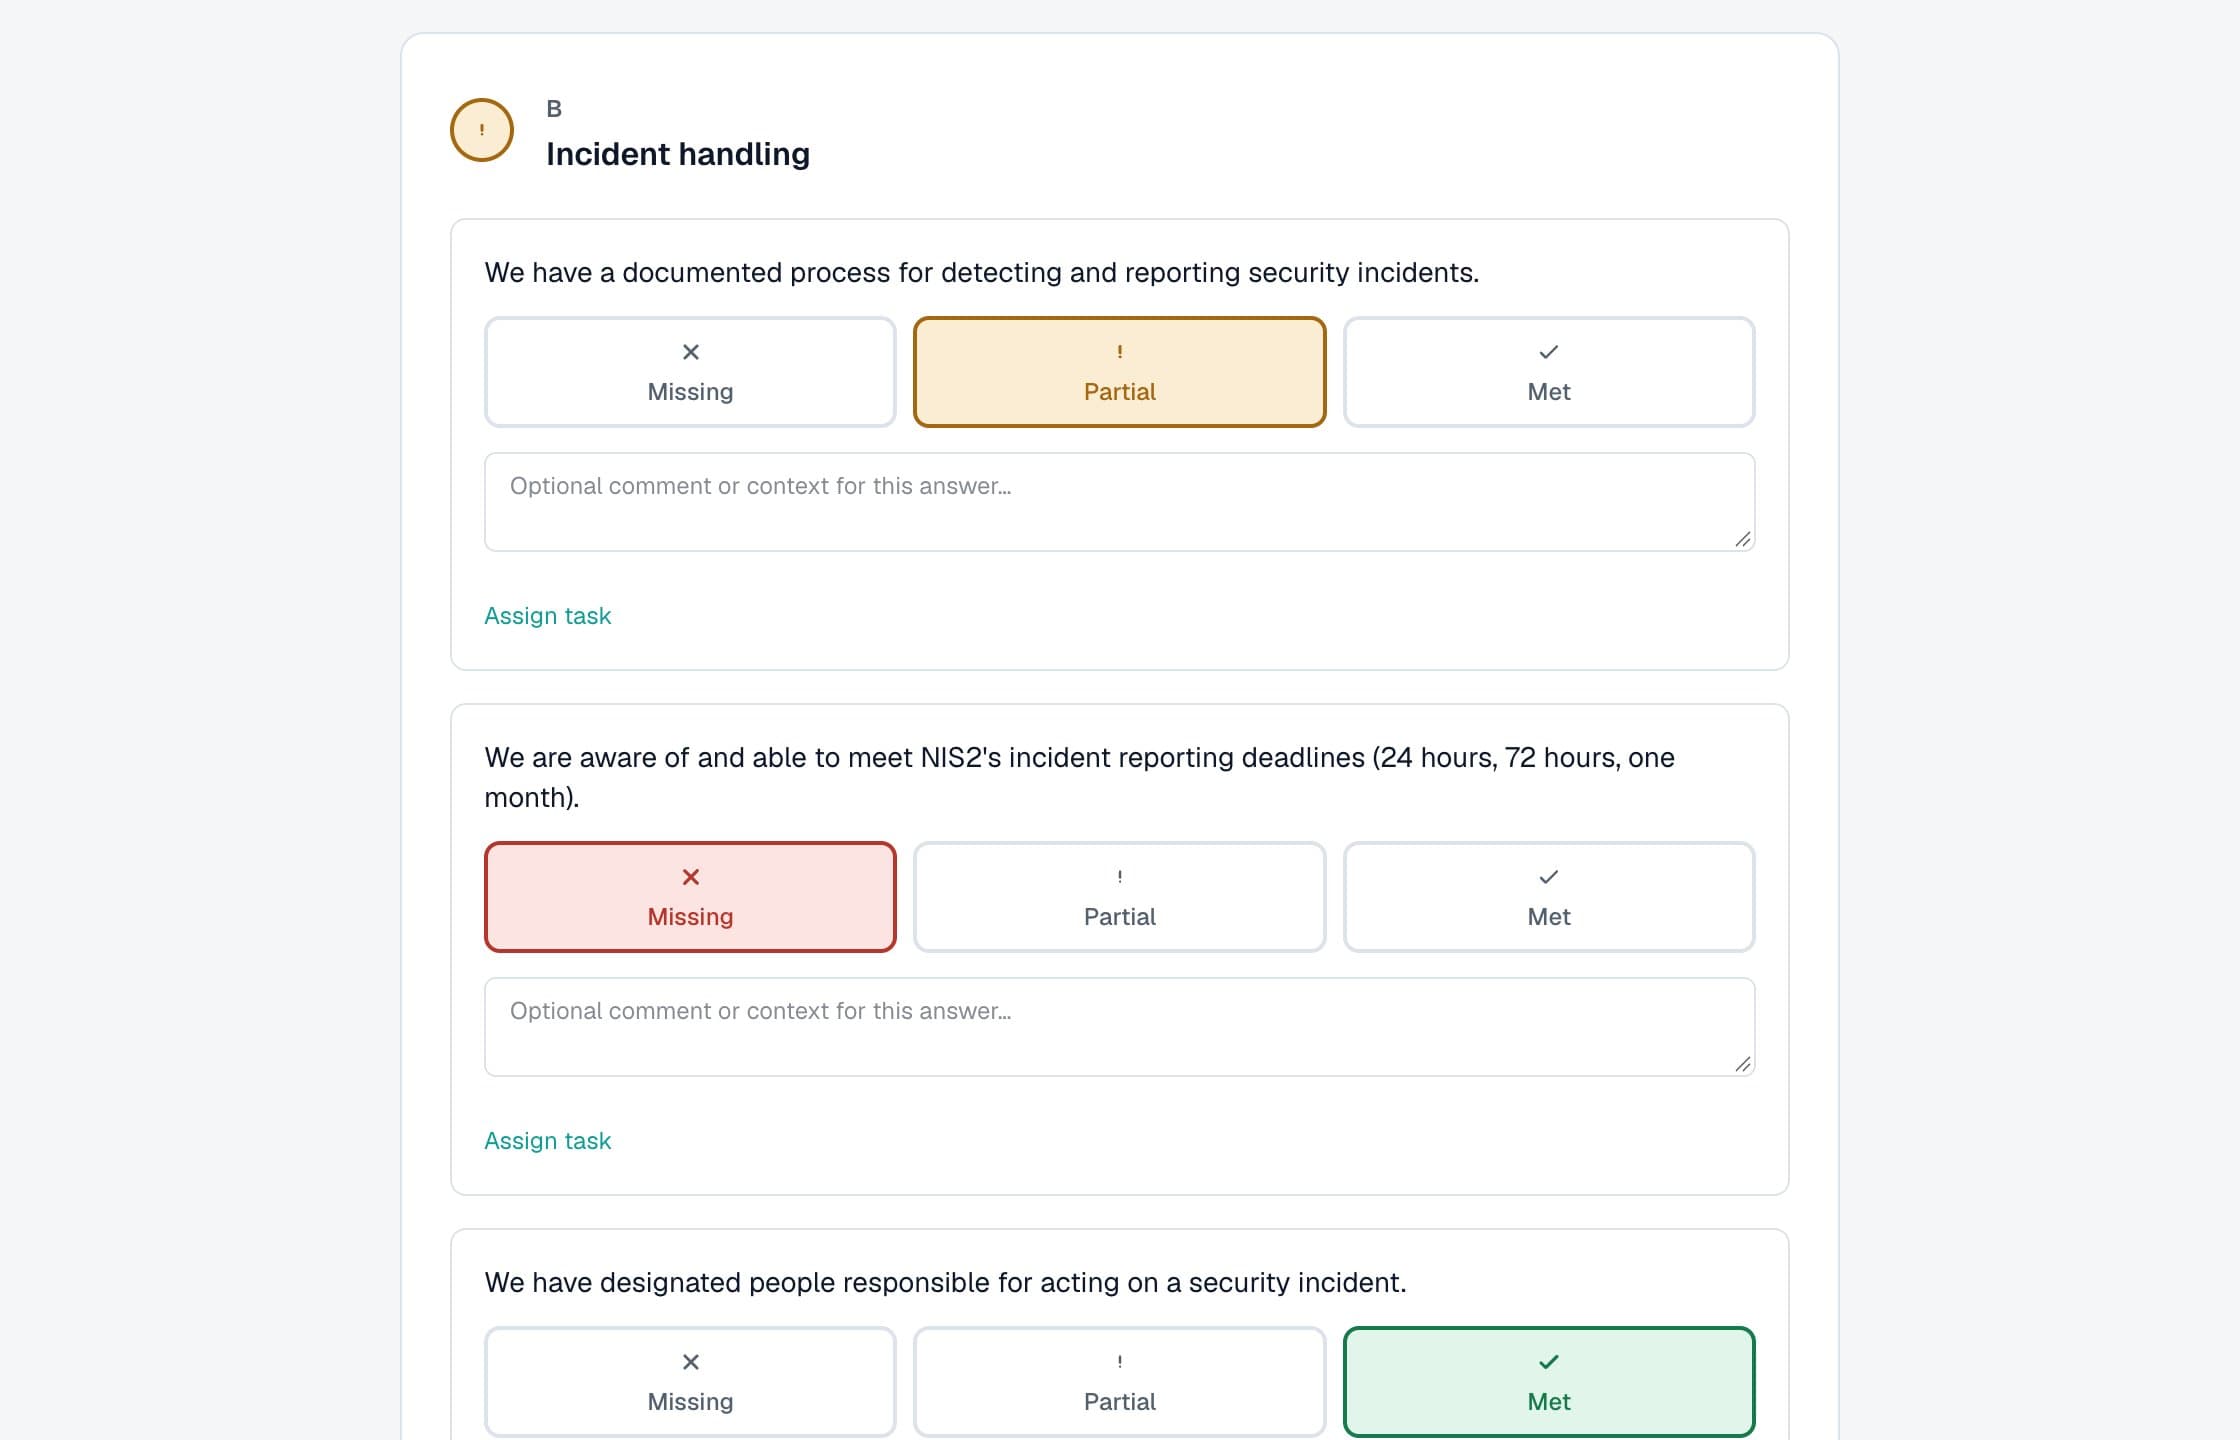
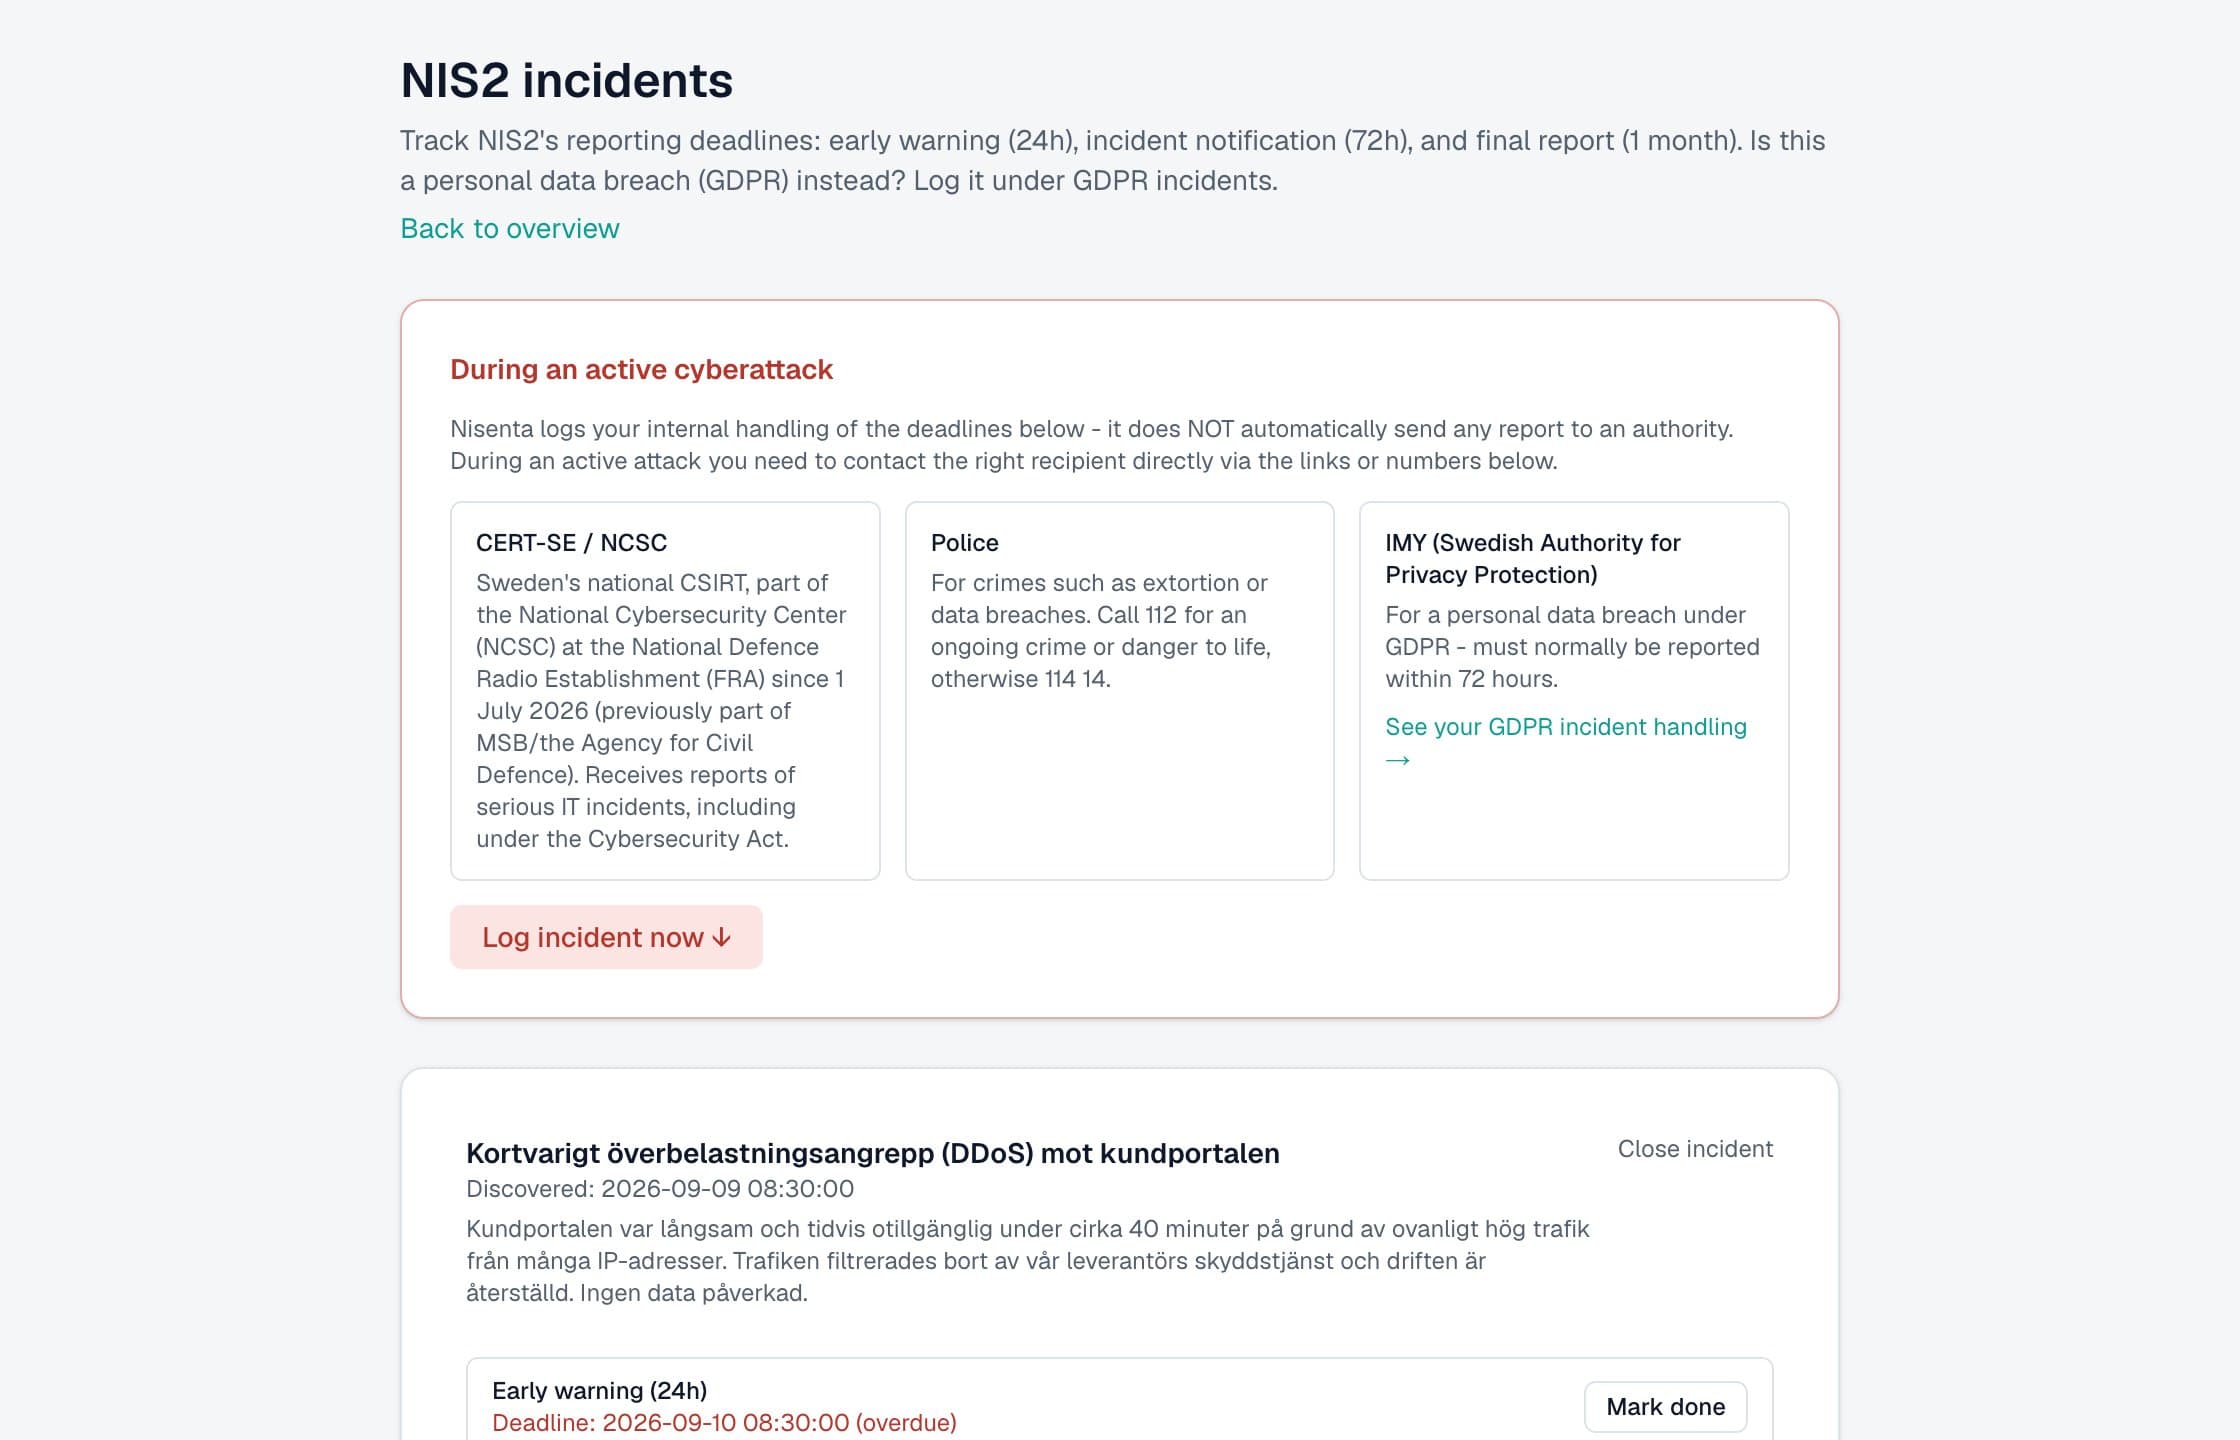
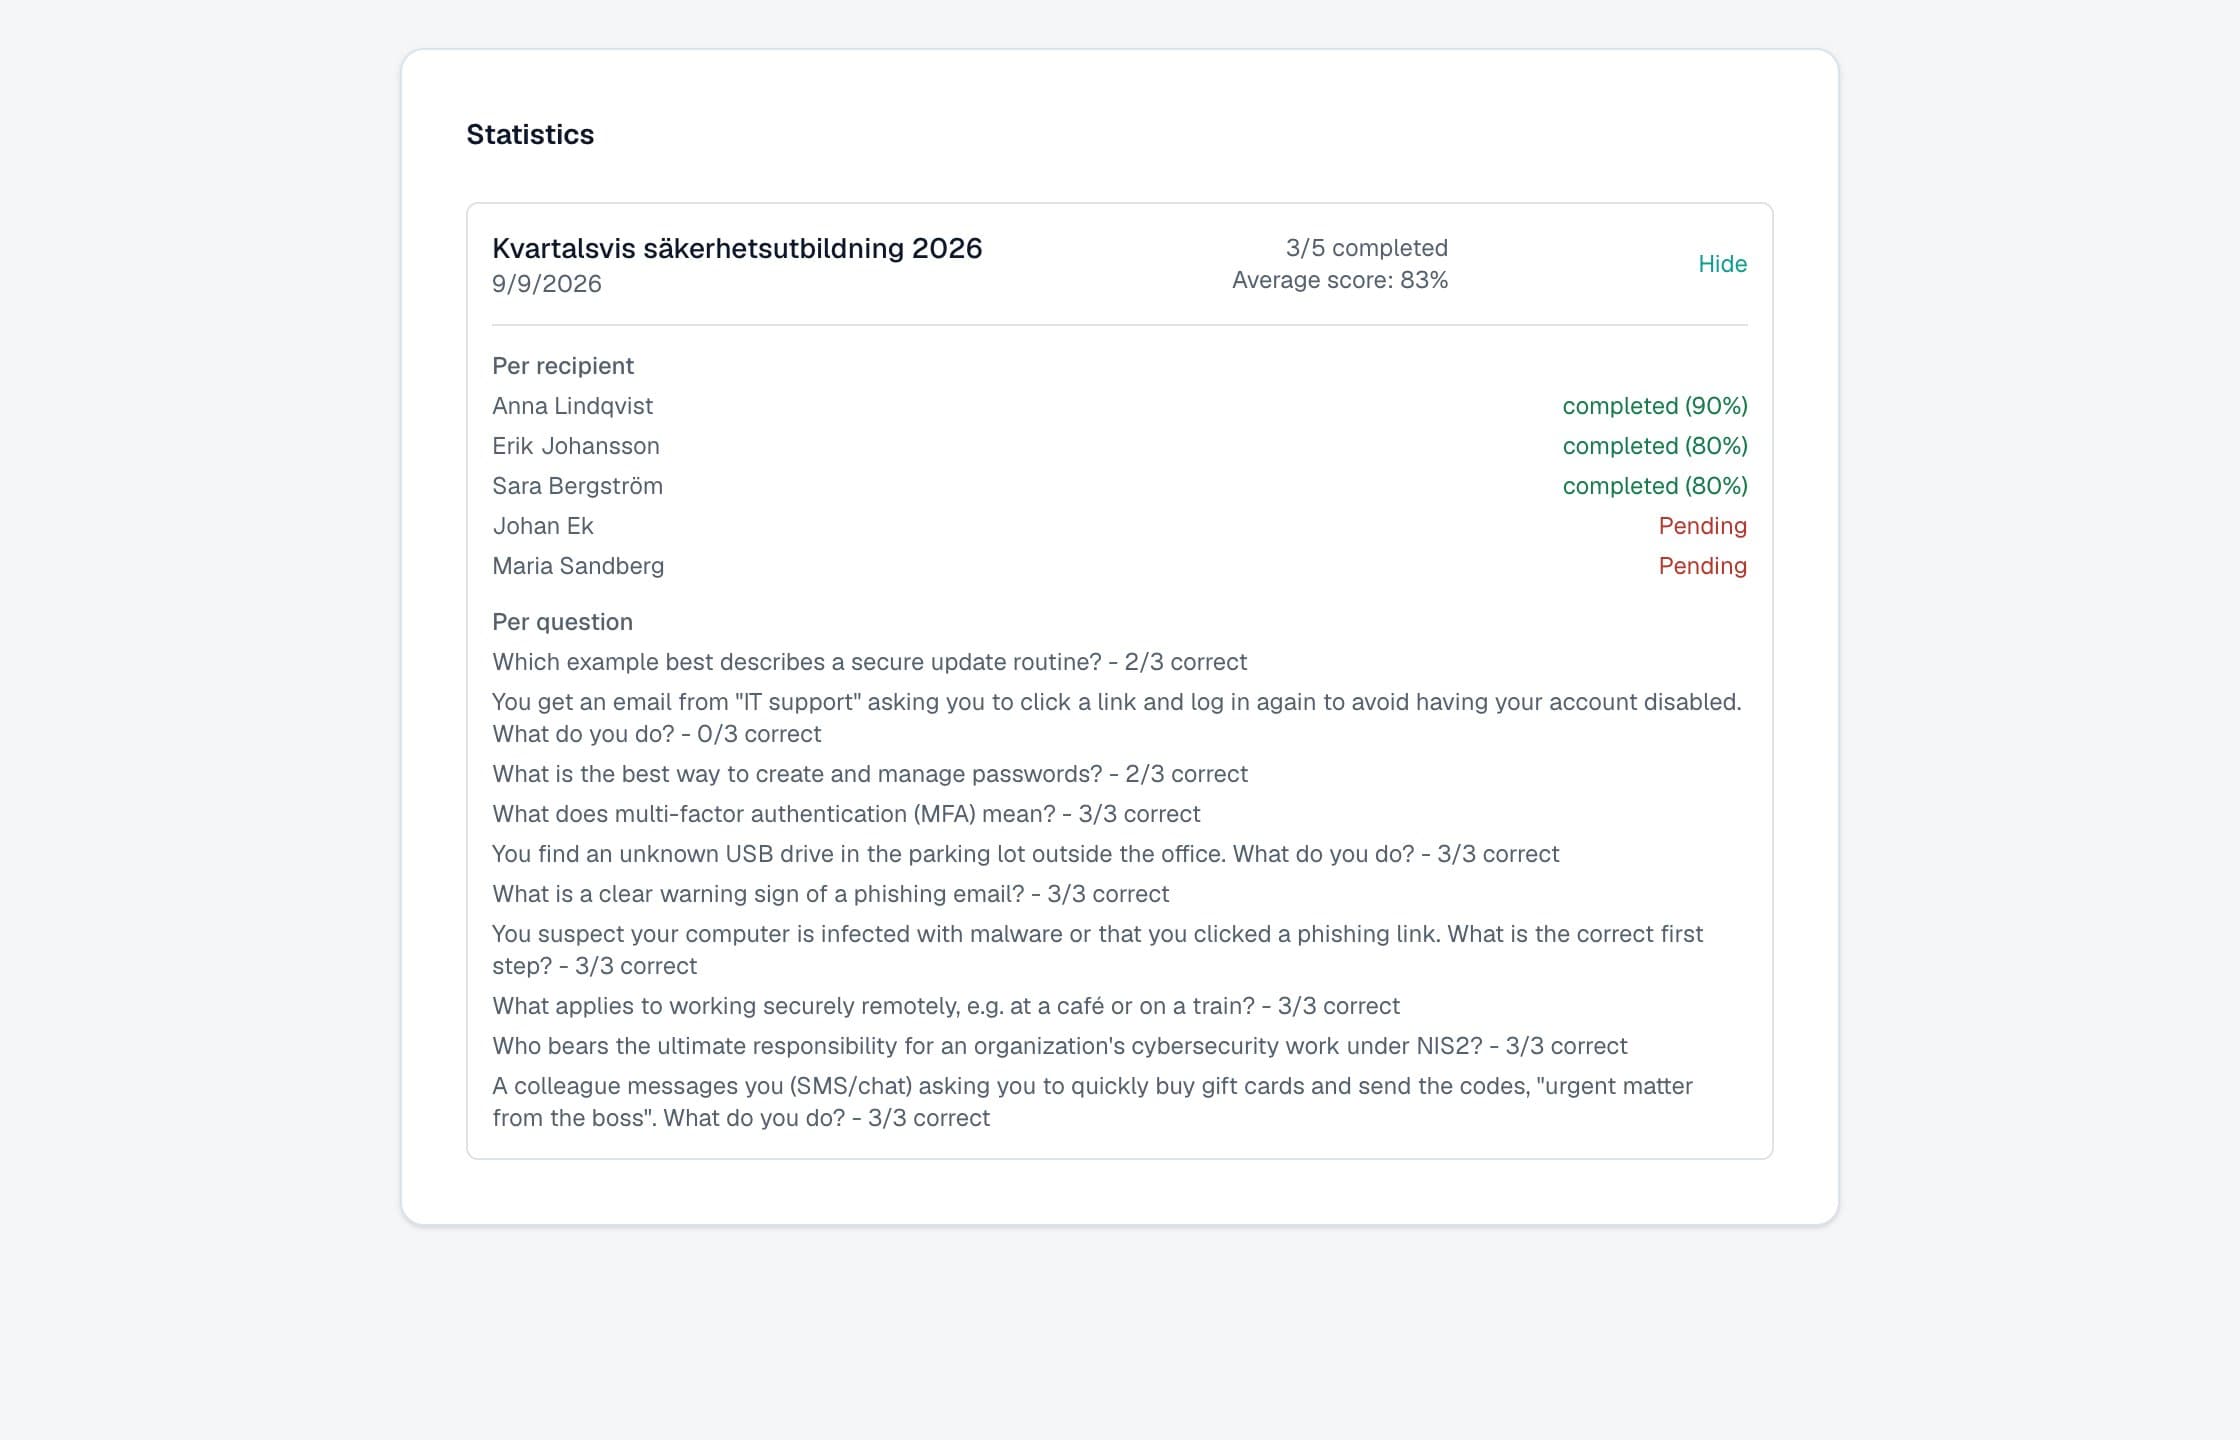
Overview. Status per regulation in one view.
Why it can't wait
NIS2 and GDPR aren't optional recommendations - they're law, with real consequences for the company and for those of you in management.
- 0 hIncident detected
- 24 hEarly warning (NIS2)
- 72 hFormal notification (NIS2) · report to IMY (GDPR)
Personal liability for management
Under NIS2, the board must approve risk-management measures and undergo training - and can be held personally liable for gross negligence.
Significant fines
Non-compliance with either NIS2 or GDPR can lead to very expensive fines - the penalties scale with company turnover, not a small fixed amount.
Tight incident deadlines
NIS2 requires an early warning within 24 hours and a formal notification within 72 hours. GDPR requires notifying the supervisory authority within 72 hours. Without a routine, you won't make it.
What you get out of it
Compliance that brings order to everyday work, not just a document for the supervisory authority.
Less administration
Requirements, evidence, reminders and history in one place instead of in emails and spreadsheets.
Predictable cost
A fixed monthly fee instead of consultant hours every time the requirements change.
Better control
See at a glance what is missing, who owns it and what has happened since last time.
Easier board reporting
Download a combined report when the board or the auditor asks.
Everything you need to show you're on top of it
Built around the actual requirements in the regulations, not generic checklists.
Feature and regulation
Gap analysis against NIS2 Article 21
All ten requirement areas - risk analysis, incident handling, supply chain, encryption and more - with a clear red/yellow/green status per area.
- NIS2NIS2
GDPR compliance in the same view
Lawful basis, data subject rights, processor agreements and incident handling are assessed in the same engine as NIS2, without becoming a separate product.
- GDPRGDPR
Combined reports on demand
Download a PDF report showing the full picture across NIS2 and GDPR in one document - ready for a board meeting or an audit.
- NIS2NIS2
- GDPRGDPR
Security awareness training
Build a question bank, send out quizzes on a recurring schedule, and see response rates and results per round.
- NIS2NIS2
Supplier follow-up
Invite your suppliers to answer a simplified form via a one-time link, with no account required on their end.
- NIS2NIS2
Incident handling with the right contacts
Quick contacts to the right authority and clear deadlines built right into the platform, so you act in time when something happens.
- NIS2NIS2
- GDPRGDPR
As your business grows, the platform grows with it
CRA (Cyber Resilience Act)
An add-on for manufacturers and sellers of products with digital elements. Assess each product separately against the EU's product security requirements.
- CRACRA
ISO 27001 / 27002 guidance
Recommendations and control mapping against the gap analysis categories, for those who want to structure the work around the ISO standard.
Guidance based on ISO standard
Why Nisenta?
How the most common ways of working with NIS2 and GDPR compare.
Cost
NisentaFixed, from SEK 990/month
- Consultant
- Hourly rate per assignment
- Excel
- Free, but costs time
- Large GRC platform
- High licence and rollout
Built for NIS2 and GDPR
NisentaYes
- Consultant
- Varies
- Excel
- No, you build it yourself
- Large GRC platform
- Often generic
Follow-up over time
NisentaYes
- Consultant
- With each new assignment
- Excel
- Manual
- Large GRC platform
- Yes
Getting started
NisentaSame day
- Consultant
- Weeks
- Excel
- Immediately, but without structure
- Large GRC platform
- Months
| Criterion | Consultant | Excel | Large GRC platform | Nisenta |
|---|---|---|---|---|
| Cost | Hourly rate per assignment | Free, but costs time | High licence and rollout | Fixed, from SEK 990/month |
| Built for NIS2 and GDPR | Varies | No, you build it yourself | Often generic | Yes |
| Follow-up over time | With each new assignment | Manual | Yes | Yes |
| Getting started | Weeks | Immediately, but without structure | Months | Same day |
General comparison. Set-ups and prices vary between providers.
See pricingHow it works
From registration to a report you can show off - no consultant, no spreadsheets.
- 01
Register your company
Create an account in a few minutes, no installation or IT integration required.
- 02
Answer the gap analysis
Mark where you stand per requirement: met, partial, or missing - with the option to attach evidence.
- 03
Remediate and train
Assign tasks to the right person and send out security awareness training on a recurring schedule.
- 04
Report
Download a combined report whenever you need to show off your status - internally or for an auditor.
Ready to get started?
Register your company today, or become a reseller and help your customers get ready for NIS2 and GDPR.